Exposed Since Screensaver
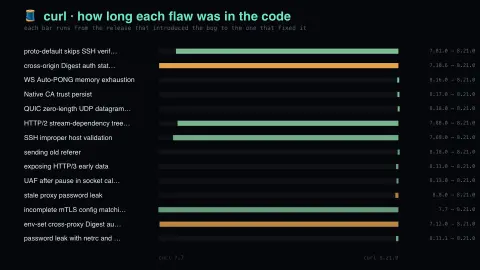
The Exposed Since screensaver shows curl’s complete vulnerability history drawn as version spans, key-less. It’s free, runs in your browser, and ESC exits.
Live preview
Press ESC to leave fullscreen. Settings are saved in your browser only.
How the Exposed Since screensaver works
The saver reads the source described above and draws it on a canvas — no account, no tracking.
curl’s complete vulnerability history drawn as version spans, key-less. Each record names both the release a flaw entered in and the one that removed it, so every bar is the window during which shipping code on billions of devices carried it.
It refreshes on a schedule, so what you see stays current.
Colours and any options can be changed in settings; nothing is stored beyond your own browser.
Counting how long a flaw lived
curl is a widely used command-line tool and library for transferring data over network protocols, maintained as an open-source project led by Daniel Stenberg. It is embedded in a very large range of software, which is one reason its security history gets close attention.
The project publishes its vulnerability records as a JSON file in the OSV (Open Source Vulnerabilities) schema. Each record has an identifier and CVE alias, a summary, and a severity label of Low, Medium or High. It also has an affected-versions section whose ordered events name the version where the flaw was introduced and the version that fixed it. This saver draws each flaw as a span across releases, from the version that brought it in to the one that removed it.
Some records list several spans, one for each release branch. The length of a bar is measured in releases, not calendar time. A long span shows that a bug went unnoticed through many versions, not that it was widely exploited, and the severity labels are the project’s own judgement.
A worked example
curl’s complete vulnerability history drawn as version spans, key-less. Each record names both the release a flaw entered in and the one that removed it, so every bar is the window during which shipping code on billions of devices carried it.
Settings & tips
- Accent and Background recolour the display.
- Every value on screen comes from the live source — nothing is simulated.
- Press ESC to leave fullscreen.
Frequently asked questions
- Is this real data?
- Yes — it comes from the source named on this page and is refreshed on a schedule.
- Is a key needed?
- No. This source is fully key-less.
- Is it free?
- Yes, and it runs entirely in your browser.
- Why does the feed show the version that introduced the bug?
- curl’s records, published in the OSV schema, name both the introduced and fixed versions explicitly, which lets the saver draw a bug’s lifespan.
- Does a long bar mean the flaw was actively exploited?
- No. It only means the flaw went unnoticed for many releases, and says nothing about exploitation in the wild.